Established event, disputed explanations
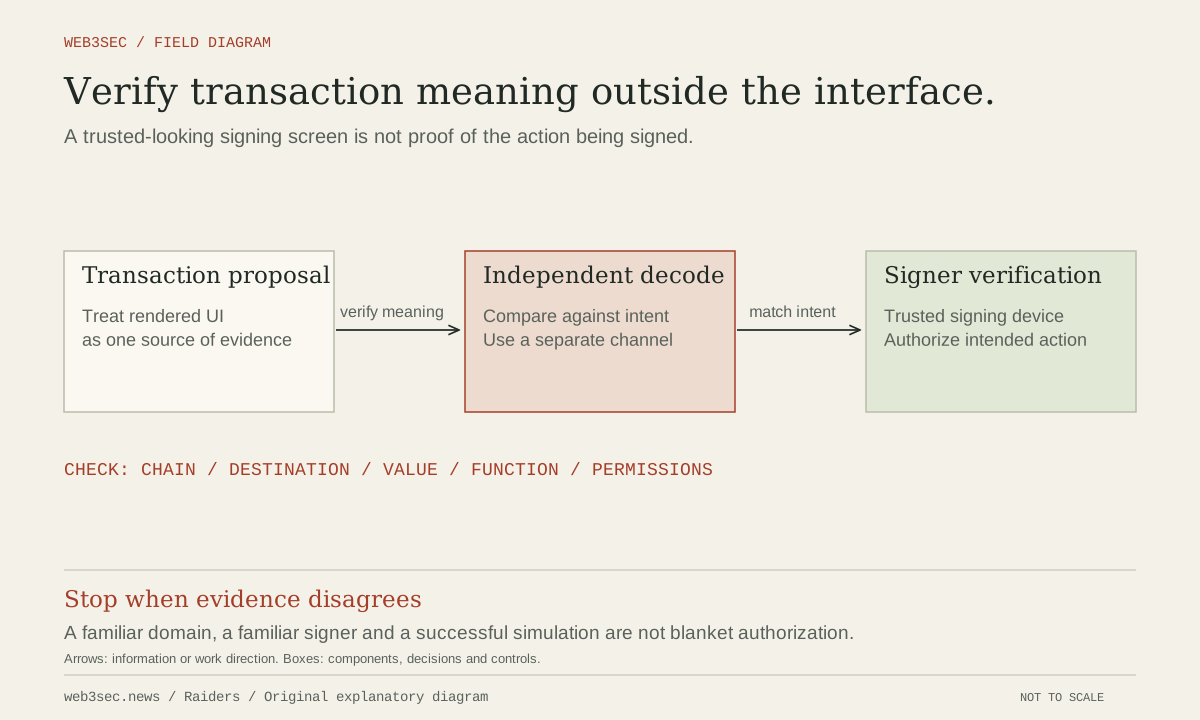
WazirX reported that a multisig wallet was attacked on 18 July 2024, with more than $230 million in digital assets stolen. Its published statements discuss a wallet accessed through Liminal infrastructure and describe a mismatch between expected transaction behavior and the transaction that was approved.
Liminal published a different account of responsibility, stating its platform remained secure and pointing to a customer-level compromise. These party statements should not be collapsed into a definitive, independently proven root cause. This analysis does not resolve that dispute or describe current customer recovery outcomes.
Turn contractual assurances into observable controls
Our analysis: an organization needs evidence of what a custody policy actually enforces. For each signing path, document who constructs the transaction, who decodes it, where allowlists are enforced, which operations bypass ordinary transfer rules and who can change those policies.
In a non-production environment, test an unexpected destination, an implementation change and an approval request outside normal working patterns. Record whether the restriction is enforced by a contract, a signing service or a user interface. Those controls have different trust assumptions and failure modes.
Prepare for a service interruption
Wallet compromise can become a customer operations problem immediately. Prepare a decision tree for deposits, withdrawals and trading that accounts for incomplete information. A public status message should identify the affected scope, action being taken and next update time without presenting guesses as conclusions.
Maintain an evidence-sharing process with service providers before an incident. Agree on access to logs, retention, escalation contacts and preservation steps. Test those arrangements during a joint exercise rather than discovering their limits while funds are moving.
Controls to take away
- Test policy enforcement at the actual signing boundary.
- Agree on evidence access and provider escalation in advance.
- Keep disputed claims clearly attributed in incident communications.
Sources & further reading
Incident facts are attributed to the reports below. Controls and recommendations are our interpretation; this is not an independent forensic investigation.
A correction or a better primary source? Send Raiders the article URL and evidence. Editorial policy.