The published advisory
Red Hat’s CVE-2024-3094 advisory describes malicious code in upstream XZ release tarballs beginning with version 5.6.0. The build process extracted a concealed object from test material and modified liblzma. The advisory identifies the malicious release packages as 5.6.0 and 5.6.1 and states that Red Hat Enterprise Linux versions were not affected.
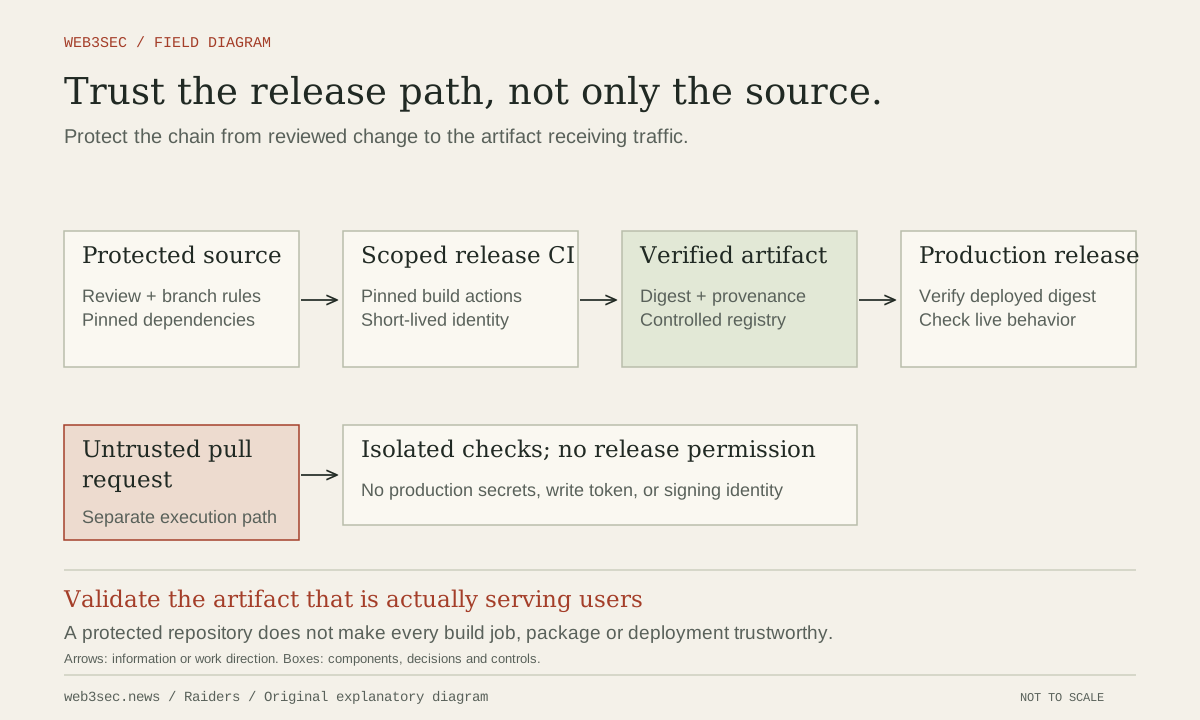
This matters because the release package and its build behavior are part of the product’s trust boundary. A review that considers only familiar source files can miss code introduced through packaging and generated build inputs.
Treat release inputs as security-relevant code
Our analysis: compare release tarballs with their corresponding source revision. Explain generated files, binary fixtures and build-system differences. A test asset that becomes executable input deserves the same scrutiny as a script.
Record the origin and digest of operating-system packages, container base images and application dependencies. A lockfile for JavaScript dependencies does not inventory the compiler, image packages or installation scripts that also participated in producing the deployed site.
A practical response path
When a dependency compromise is disclosed, identify affected deployed artifacts using exact package and distribution information. Follow the relevant vendor’s remediation guidance; version numbers alone can be misleading when distributors backport fixes or replace packages.
For confirmed affected systems, replacing the package is only one response step. Assess whether the system was exposed, which identities it held and whether rebuild or credential invalidation is warranted. Preserve enough build provenance that responders can answer those questions without reconstructing the release from memory.
Controls to take away
- Review release packaging and generated build inputs.
- Inventory system packages as well as application dependencies.
- Retain provenance for the artifacts actually deployed.
Sources & further reading
Incident facts are attributed to the reports below. Controls and recommendations are our interpretation; this is not an independent forensic investigation.
A correction or a better primary source? Send Raiders the article URL and evidence. Editorial policy.